Fraudulent COVID-19 emails specifically target Canadians, security firm says

Advertisement

Advertise with us

TORONTO - Cybersecurity experts are renewing their warnings that the COVID-19 crisis is a huge opportunity for criminals to take advantage of confusion as people are forced to work away from the office.

Read this article for free:


or

Already have an account? Log in here »

To continue reading, please subscribe:

Subscribe and receive a limited-edition Free Press branded hat or tote.

Digital Subscription

One year of digital access for only $205*

  • Enjoy unlimited reading on winnipegfreepress.com
  • Read the E-Edition, our digital replica newspaper
  • Access News Break, our award-winning app
  • Play interactive puzzles

*First annual payment billed as $205.00 + GST for one year. This annual subscription will automatically renew at $233.00 + GST every 52 weeks (10% off the regular annual price of $259.35). Offer available to new and qualified returning subscribers only. Cancel any time.

To continue reading, please subscribe:

Add Free Press access to your Brandon Sun subscription for only an additional

$1 for the first 4 weeks*

  • Enjoy unlimited reading on winnipegfreepress.com
  • Read the E-Edition, our digital replica newspaper
  • Access News Break, our award-winning app
  • Play interactive puzzles
Start now

*Your next Brandon Sun subscription payment will increase by $1.00 and you will be charged $17.95 plus GST for four weeks. After four weeks, your payment will increase to $24.95 plus GST every four weeks.

Hey there, time traveller!
This article was published 18/03/2020 (2387 days ago), so information in it may no longer be current.

TORONTO – Cybersecurity experts are renewing their warnings that the COVID-19 crisis is a huge opportunity for criminals to take advantage of confusion as people are forced to work away from the office.

A U.S. security firm says at least two shadowy criminal groups are specifically targeting Canada with faked emails that pretend to provide updated information about the novel coronavirus.

One example collected by California-based Proofpoint pretends to be from the Public Health Agency of Canada but it refers to a real official from another organization and has a fake email address.
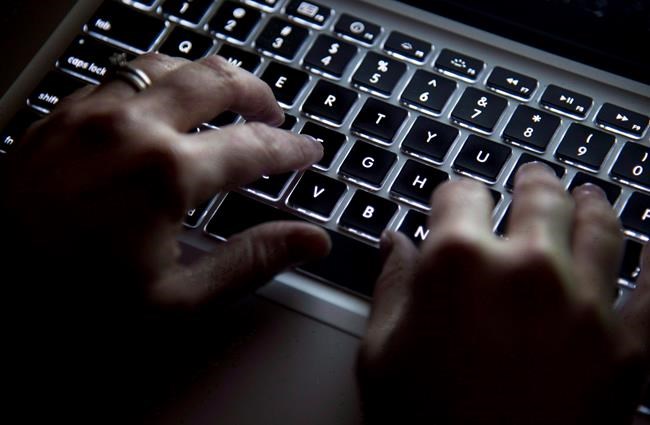
Hands type on a keyboard in North Vancouver, B.C., on Wednesday, December, 19, 2012. A U.S. security firm says at least two shadowy criminal groups are specifically targeting Canada with huge numbers of faked emails that pretend to provide updated information about coronavirus.THE CANADIAN PRESS/Jonathan Hayward

Proofpoint executive vice-president Ryan Kalember says the criminal groups, which he calls threat actors, know people have a lot to think about right now and may have their guard down.

“And people click on things,” Kalember says. “Everyone is looking for information and updates … to be communicated from the executives of their own company.”

Although the Canadian example provided by Proofpoint is fairly clumsy and easy to detect, there have been well-crafted emails that seem to be a company president’s message to all staff.

David Masson, Ottawa-based director of threat intelligence for Darktrace, says employees are more vulnerable to cyber tricks “when they’re out and about” and not inside their headquarters.

“Right now we’re seeing an explosion of hundreds of thousands, if not millions, of people suddenly working from home for the first time,” Masson says.

“That’s an issue because it’s easier for them to be exploited.”

A spokesman for eSentire — an Ontario-based private company that manages threat detection and response for organizations in several countries — says criminals “can prosper and grow in chaos.”

The criminals know some organizations weren’t prepared for the impact of COVID-19 and are now playing emergency catch-up, says eSentire vice-president Mark Sangster.

“And those are the times to strike,” Sangster adds.

His advice for employees: don’t share information gathered from friends, social media or suspicious email with attachments because that could spread malevolent software through the organization.

“You’re controlling the potential for misinformation because that’s where people end up clicking on fake links or opening fake documents,” Sangster says.

As for organizations, he says they need to provide daily or weekly updates as necessary.

“So employees feel comfortable and there is no confusion around what they must or must not do.”

Sangster also warns that an organization’s overall security protection is weaker if some devices are consumer-grade equipment, such as a router provided by an employee’s internet service provider.

“It’s a good device. But it’s certainly not hardened to the level of commercial, enterprise-type equipment,” Sangster says.

He advises companies to use some kind of secure connection back to their head offices — a virtual private network (VPN).

“That technology effectively encrypts the communications back and forth, so that whoever’s snooping or tries to capture information can’t see it, doesn’t know what it is,” Sangster says.

As for the types of anti-virus software used by most consumers, Sangster says they’re necessary but won’t stop the types of emails that tempt people to click on fraudulent documents or links.

“And unfortunately,” Sangster says, “the kind of tools and technologies that typically are going to do that are that are ones that are going to reside in the corporate head office.”

This report by The Canadian Press was first published March 18, 2020.

Report Error Submit a Tip

More Stories

What does the PC stand for in party’s name? Seems to be Pretty Confused

Tom Brodbeck 5 minute read Preview

What does the PC stand for in party’s name? Seems to be Pretty Confused

Tom Brodbeck 5 minute read Yesterday at 1:11 PM CDT

It should have been obvious from the beginning that the Manitoba Progressive Conservative party was going to have trouble holding itself together under Obby Khan.

The warning came in April 2025, when the now-former PC party leader narrowly won the leadership over far-right populist candidate Wally Daudrich.

Technically, Khan won. Politically, however, it was a more complicated result.

Daudrich received more votes than Khan, but Khan prevailed because the party used a constituency-weighted points system that gave him just enough of an advantage to put him over the top.

Read
Yesterday at 1:11 PM CDT

WP Router Placeholder Page

0 minute read Thursday, Dec. 22, 2022

Bombers look to lock in to post-season chase after dropping game to Argos

Taylor Allen 6 minute read Preview

Bombers look to lock in to post-season chase after dropping game to Argos

Taylor Allen 6 minute read Monday, Sep. 28, 2026

The Winnipeg Blue Bombers let a major opportunity slip through their fingers, and they know it.

“F—- yeah. That game was ours,” said defensive end Willie Jefferson on Friday’s 30-28 loss at home to the Toronto Argonauts.

It was — and then they gave it away in the final five minutes.

The Bombers came out firing, jumping out to a 21-7 lead. They had a chance to close out the contest while leading 28-27 with two minutes remaining, but couldn’t do it. Quarterback Dru Brown was sacked by linebacker Adarius Pickett, forcing the Bombers to punt, and the Argos took full advantage.

Read
Monday, Sep. 28, 2026

State of the Nations event to highlight Indigenous mining plans

Gabrielle Piché 3 minute read Preview

State of the Nations event to highlight Indigenous mining plans

Gabrielle Piché 3 minute read Monday, Sep. 28, 2026

A first-ever conference aims to connect Indigenous leaders with businesses as local mining ambitions grow.

The Manitoba Prospectors and Developers Association expects to rally a half-dozen chiefs to present on their communities’ mineral development projects.

The Nov. 16 event — called the State of the Nations — comes as the province promises to triple critical mineral production.

“We want to see those minerals being developed and being able to be exported,” said Renée Greyeyes, the prospectors association’s chief executive.

Read
Monday, Sep. 28, 2026

Port of Churchill signs agreement with Dutch port

Aaron Epp 2 minute read Preview

Port of Churchill signs agreement with Dutch port

Aaron Epp 2 minute read Yesterday at 4:40 PM CDT

Arctic Gateway Group, operator of the Port of Churchill, has signed an agreement with the Port of Rotterdam in the Netherlands to attract business and strengthen supply chains linking Western Canada and Europe.

The agreement enables the two ports to work together to develop new trade in critical minerals and energy products, connect Canadian producers with European buyers, and identify opportunities to improve the supply chain from Western Canadian resource projects through Churchill and into European markets.

The Port of Rotterdam is Europe’s largest port and home to more than 3,000 businesses across its industrial complex, serving as a major gateway for critical raw materials and energy.

Meanwhile, the Port of Churchill has been identified as a transformative national strategy for Canada and is emerging as a northern trade corridor connecting Western Canada’s resources to global markets.

Read
Yesterday at 4:40 PM CDT

Plenty of losses all around

Gwynne Dyer 4 minute read Wednesday, Jul. 15, 2026

The last time oil-tankers were being shot up in the Persian Gulf, back in the 1980s, it was Saddam Hussein’s brutal tyranny in Iraq versus Ayatollah Khomeini’s revolutionary Islamist regime in Iran.

The United States backed Saddam because he was just another murderous thug, whereas the new regime in Tehran was an actual threat to American interests. It had overthrown Iran’s American-backed puppet king and wanted to spread its Islamist ideology across the region.

So, of course, Ronald Reagan’s administration chose Saddam’s side. It sent Iraq arms by clandestine means (because Congress wouldn’t authorize it) and even provided targeting information for Iraqi poison gas attacks on Iran. The Americans chose the “lesser evil,” but at least they knew it was evil.

Once in a while they would even say it out loud, quoting U.S. diplomat Henry Kissinger: “It’s a shame that both sides can’t lose.” But they never did anything about it, and after eight years of slaughter, the war ended in a no-score draw.